Secure authentication
SSR authentication with protected routes, cookie-based sessions and password recovery flows.
Travel SaaS / Full stack · In progress
A travel-planning product in progress, connecting authentication, saved trips and pre-travel preparation in one experience.
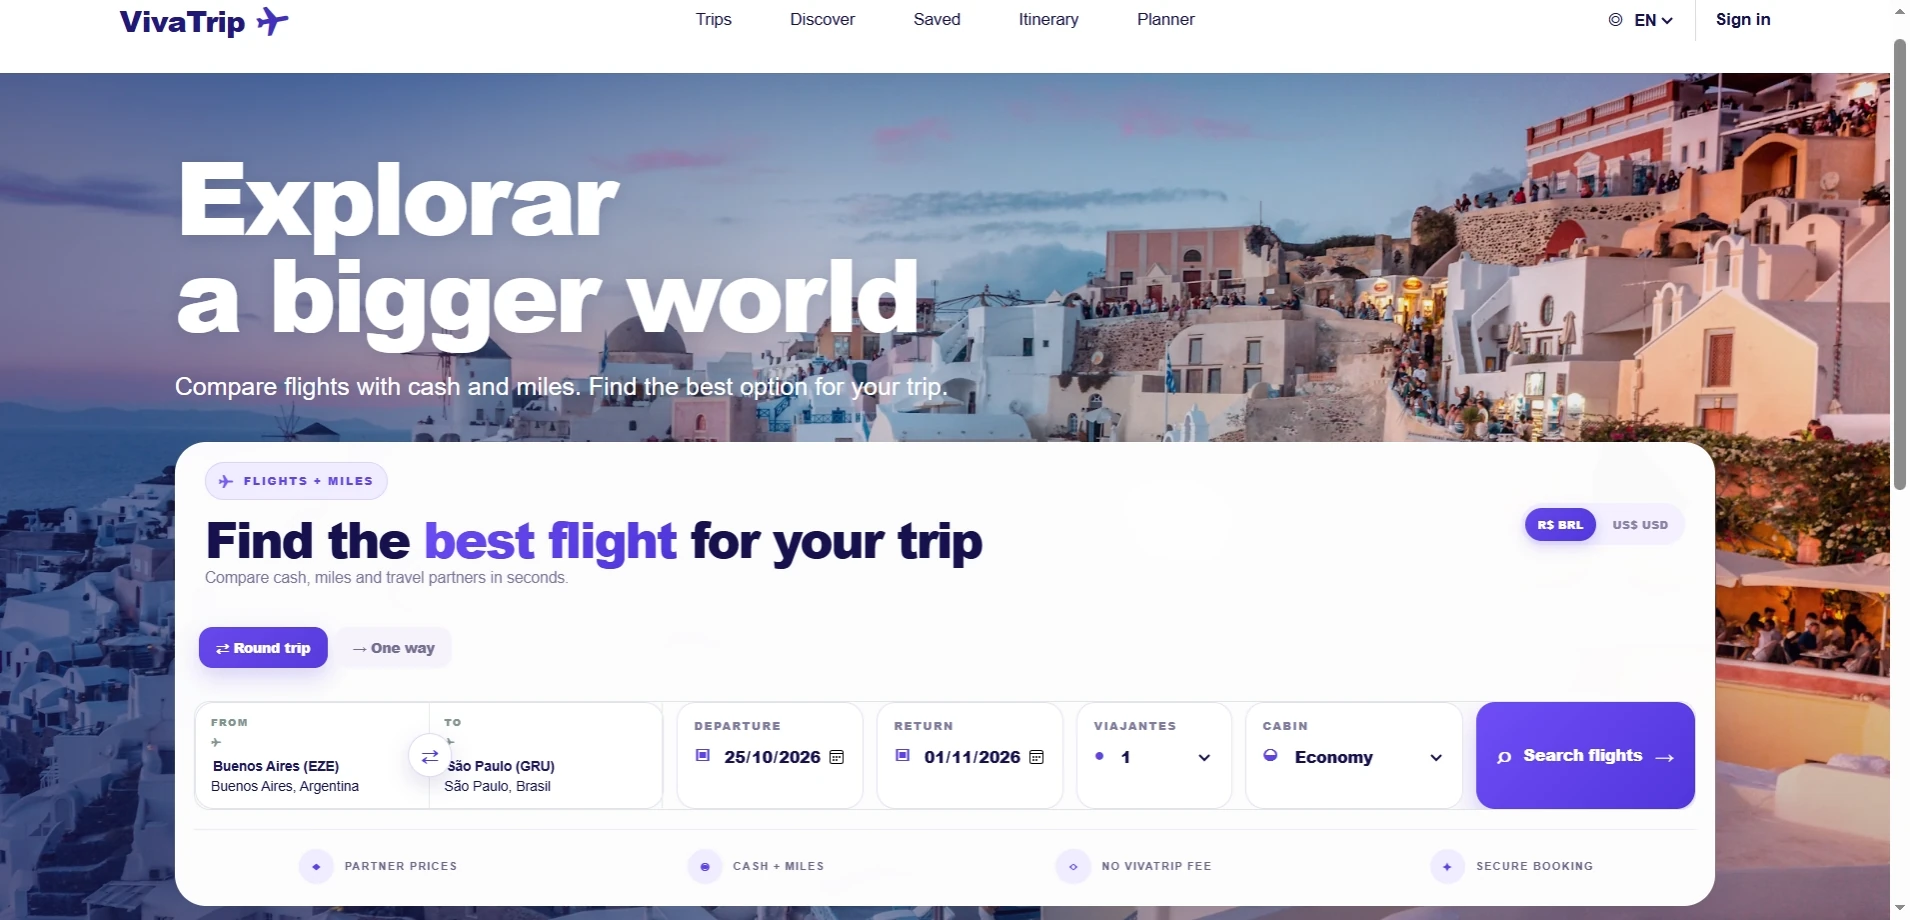
The challenge
SSR authentication with protected routes, cookie-based sessions and password recovery flows.
Trip data feeds planning screens directly, reducing duplicate information and keeping the experience consistent.
Checklist-driven preparation designed around the actual destination and travel context.
Structured to grow into itinerary editing, destination discovery, alerts and paid travel-planning features.
Technical highlights
Next.js App Router with protected routes
Supabase authentication and persistent sessions
Server-side auth checks for private screens
Reusable trip and profile UI components
Responsive layouts for desktop and mobile
Production deployment with Vercel
Engineering reflection
Technical challenge
The product needed private trip and profile screens without relying only on client-side redirects. The solution uses server-side session checks and protected routing so authentication is part of the application architecture.
What I learned
Saved trip data now drives destination-aware preparation instead of asking users to repeat the same information. This reinforced how data modeling directly affects UX quality.
What I would improve
The next engineering step is stronger end-to-end coverage for authentication, trip creation and itinerary flows, plus more resilient loading and error states.
Stack